
Current reference
ISO/IEC 30107-3:2023 is the current technical reference for PAD testing/reporting.
Explain Presentation Attack Detection and the bounded scope of PCEB 26/04/06.
Certificate → Standard → Capability → Public claim → Limitation.
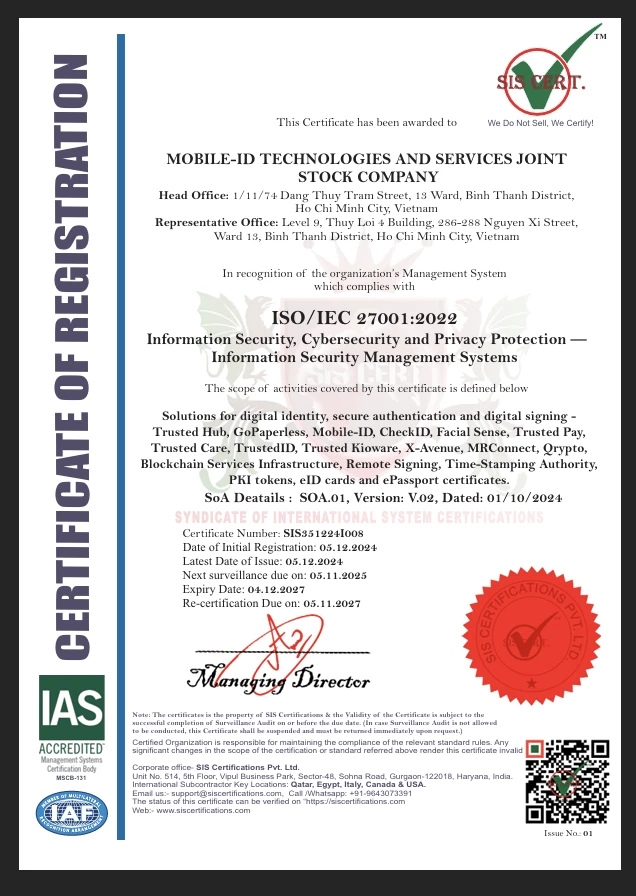
SIS351224I008
05/12/2024 → 04/12/2027
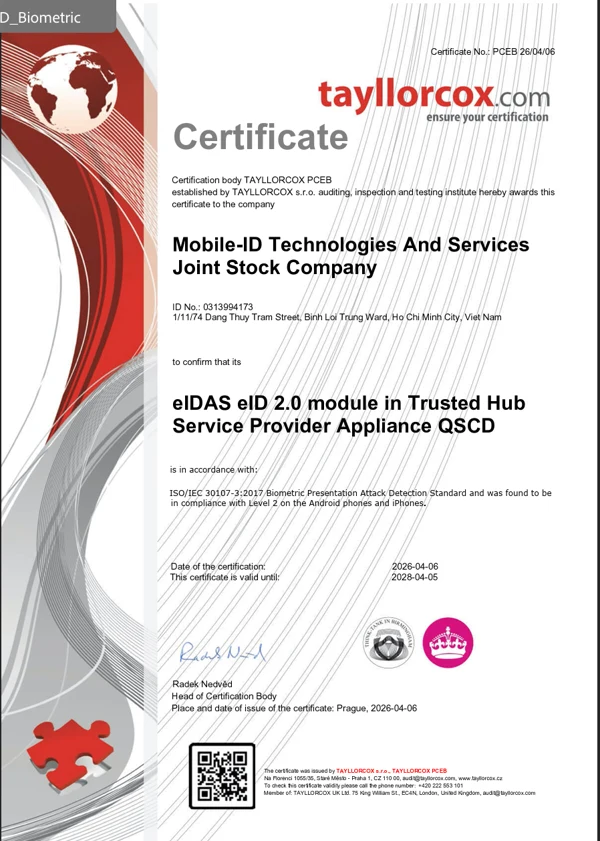
ISO/IEC 30107-3:2017
06/04/2026 → 05/04/2028
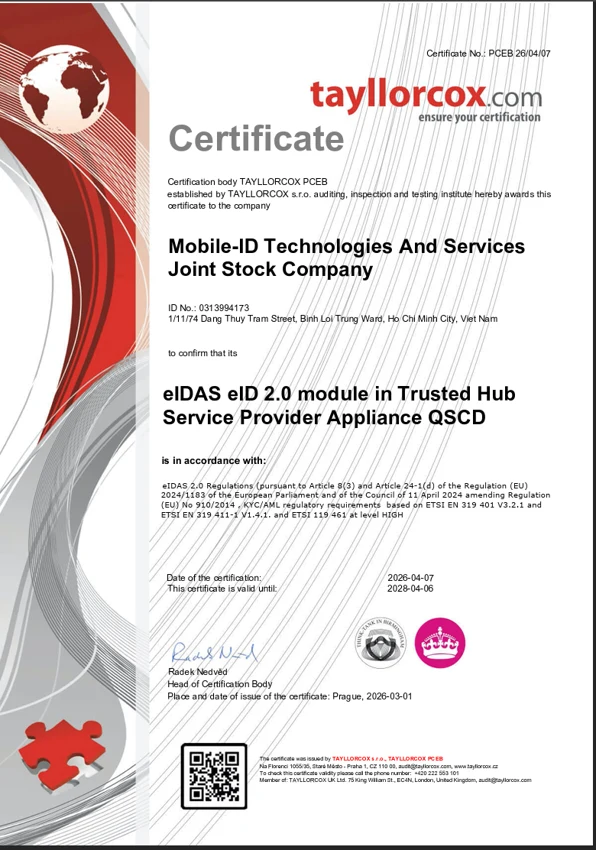
eIDAS 2.0 · ETSI
07/04/2026 → 06/04/2028
A module certificate is never generalized into a whole-service certification.
Biometric Presentation Attack Detection evaluation/reporting scope.
General policy requirements for trust service providers.
Policy/security requirements for certificate-issuing TSPs.
Identity proofing concepts, authoritative evidence/source and HIGH scope per certificate.
Source → Scope → Evidence → Limitation
ISO/IEC 30107-3:2023 is the current technical reference for PAD testing/reporting.
PCEB 26/04/06 still shows ISO/IEC 30107-3:2017 because that is the basis stated on the certificate.
The certificate covers the eIDAS eID 2.0 module in Trusted Hub Service Provider Appliance QSCD, Level 2 on Android phones and iPhones according to the certificate matrix; it is not whole-CheckID certification.
PAD presentation attacks do not automatically cover virtual camera, emulator, injection, compromised-client or channel-replay attacks.
The Trust Center publishes certificate number, subject/module, basis, certification date, expiry, platform scope and limitations.
A PAD result does not replace a biometric match result, identity-proofing result or system-level security assessment.