
Legal framework
eIDAS and Regulation (EU) 2024/1183 establish the European Digital Identity legal framework; Implementing Regulations 2024/2979 and 2024/2982 have consolidated versions dated 11 August 2026.
Map PCEB 26/04/07 to eIDAS 2.0, ETSI EN 319 401/411-1 and ETSI TS 119 461.
Certificate → Standard → Capability → Public claim → Limitation.
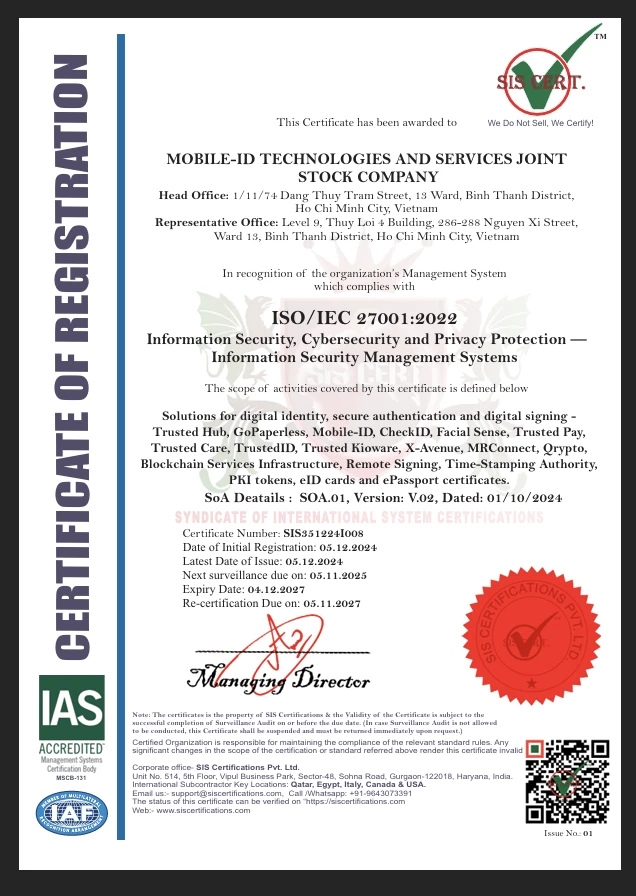
SIS351224I008
05/12/2024 → 04/12/2027
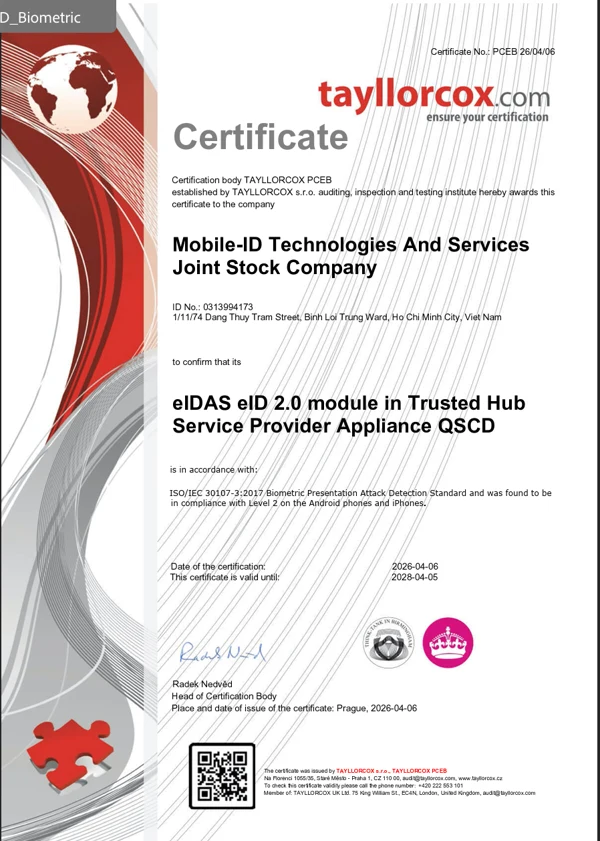
ISO/IEC 30107-3:2017
06/04/2026 → 05/04/2028
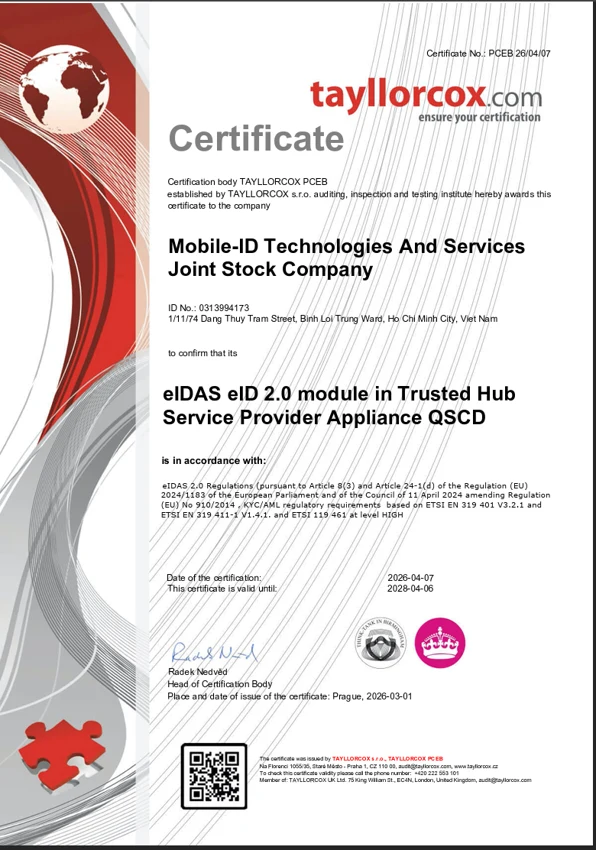
eIDAS 2.0 · ETSI
07/04/2026 → 06/04/2028
A module certificate is never generalized into a whole-service certification.
Biometric Presentation Attack Detection evaluation/reporting scope.
General policy requirements for trust service providers.
Policy/security requirements for certificate-issuing TSPs.
Identity proofing concepts, authoritative evidence/source and HIGH scope per certificate.
LAW → TECHNICAL REFERENCE → CHECKID IMPLEMENTATION → CERTIFICATION EVIDENCE
eIDAS and Regulation (EU) 2024/1183 establish the European Digital Identity legal framework; Implementing Regulations 2024/2979 and 2024/2982 have consolidated versions dated 11 August 2026.
ETSI TS 119 461 V2.1.1 is a published technical specification for identity proofing in the trust-service context. EN/draft work items are labeled with their actual status at review time.
EU 2024/2982 addresses protocols/interfaces for the EUDI Wallet framework; OpenID4VCI/VP are relevant standards-landscape references. They remain references unless CheckID implementation mapping is sourced.
PCEB 26/04/06 and PCEB 26/04/07 retain the exact certificate basis, scope, platform and validity stated on the certificates. A current standard version does not rewrite a historical evaluation basis.
Each standard is tagged IMPLEMENTED/PARTIAL/REFERENCE/NOT APPLICABLE/Requires applicability assessment from evidence; citation alone never becomes “compliant”.
A module certificate does not establish every deployment, customer journey or the entire platform. Current documentation keeps module, scope and exclusions adjacent to the claim.